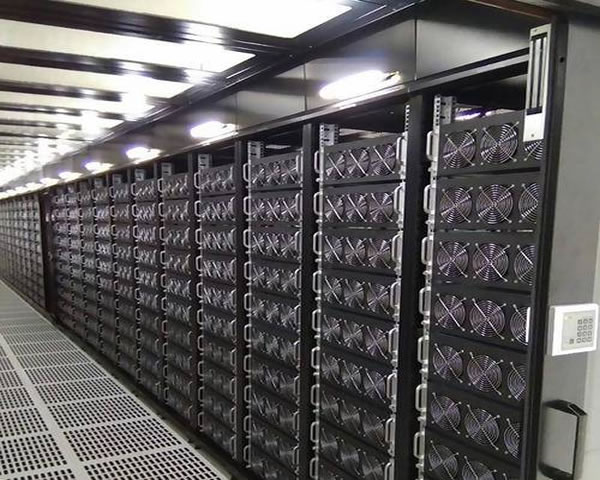
when viewing pictures of u.s. high-defense servers , you can quickly identify common protective equipment and layout points, which will help evaluate the security and protection capabilities of the computer room. this article sorts out the common physical and network protection elements in images from a professional perspective to facilitate seo retrieval and geolocation-related content, and also provides key reference for computer room design and review.
common physical protective equipment
common physical protections in the picture include fences, access control channels (mantrap), biometric card readers, and metal detection gates. high-defense computer rooms usually have reinforced cabinets, anti-pry doors, and firewall structures. these devices are the first visual clues to assess physical security and can block unauthorized physical intrusion.
network and ddos protection visibility facilities
in the high-defense server picture, common network facilities include independent cleaning equipment, dedicated firewalls and intrusion detection systems (ids/ips). multi-layer routing and switching equipment and differentiated optical fiber links can be seen in the cabinet. together with bgp or traffic cleaning architecture, they are important image indicators for identifying anti-ddos capabilities.
cooling and power redundant layout
proper cooling and power supply are shown in the picture as ups battery cabinet, diesel generator room and hot/cold aisle enclosure (hot/cold aisle). the visible redundant power distribution cabinets and pipeline wiring indicate that the computer room has an uninterrupted power supply and cooling strategy, which is conducive to maintaining the continuous operation of high-defense servers in the event of attacks or failures.
rack specifications and cabling management
cabinet locks, labeled cables, patch panels and wire troughs are intuitive features that determine the standardization of operation and maintenance. neat wiring and clear markings not only improve fault response speed, but also reduce the risk of misoperation. when looking at the pictures, pay attention to cable management and rack clearance.
monitoring, alarm and emergency response center
high-defense server pictures often show monitoring screens, noc consoles and environmental sensor panels. system logs, video monitoring and visual alarms are the core of computer room security operations. they can provide rapid positioning and response capabilities when abnormalities occur, and are an important basis for evaluating the overall protection maturity.
layout points and zoning safety principles
excellent computer room layout is reflected in partition isolation, hot and cold separation and redundant placement of key equipment. if you can see physical isolation doors, independent channels, and clear security partition marks in the picture, it usually means that fault isolation and attack mitigation have been taken into consideration in the design, which will help protect the stability of the high-defense server.
summary and suggestions
by observing the physical protection, network equipment, power supply cooling and monitoring layout in the pictures of the us high-defense servers, we can initially judge the security and protection capabilities of the computer room. it is recommended to verify details by combining multi-angle pictures and technical documents, pay attention to redundancy, partitioning and cleaning capabilities, and require equipment lists and operation and maintenance specifications to supplement the image information during procurement or evaluation.
- Latest articles
- Popular tags
-

Access Process Alipay Server Us Api Call And Callback Configuration Key Points
alipay access process and configuration points for us servers, including api calls, security signatures, callback (notify) verification, https and certificates, testing and online recommendations, to improve access success rate and stability. -

Practical Recommendations For Selecting Bandwidth And BGP Multi-Path Strategies In U.S. Independent Server Hosting Networks
Practical recommendations for network and BGP multi-link setups hosted on independent servers in the U.S., covering bandwidth assessment, billing models, port/link selection, routing strategies, redundant failover, and security compliance aspects to ensure a stable and reliable online deployment. -
Developer Guide Steps To Quickly Deploy Websites And Apis On The Candy Host Us Cloud Server
this developer guide introduces the steps to quickly deploy websites and apis on the candy host us cloud server. it covers practical suggestions such as instance selection, environment setup, security configuration, ci/cd, monitoring and backup. it is suitable for reference for teams that need to quickly go online in the us cloud environment.